
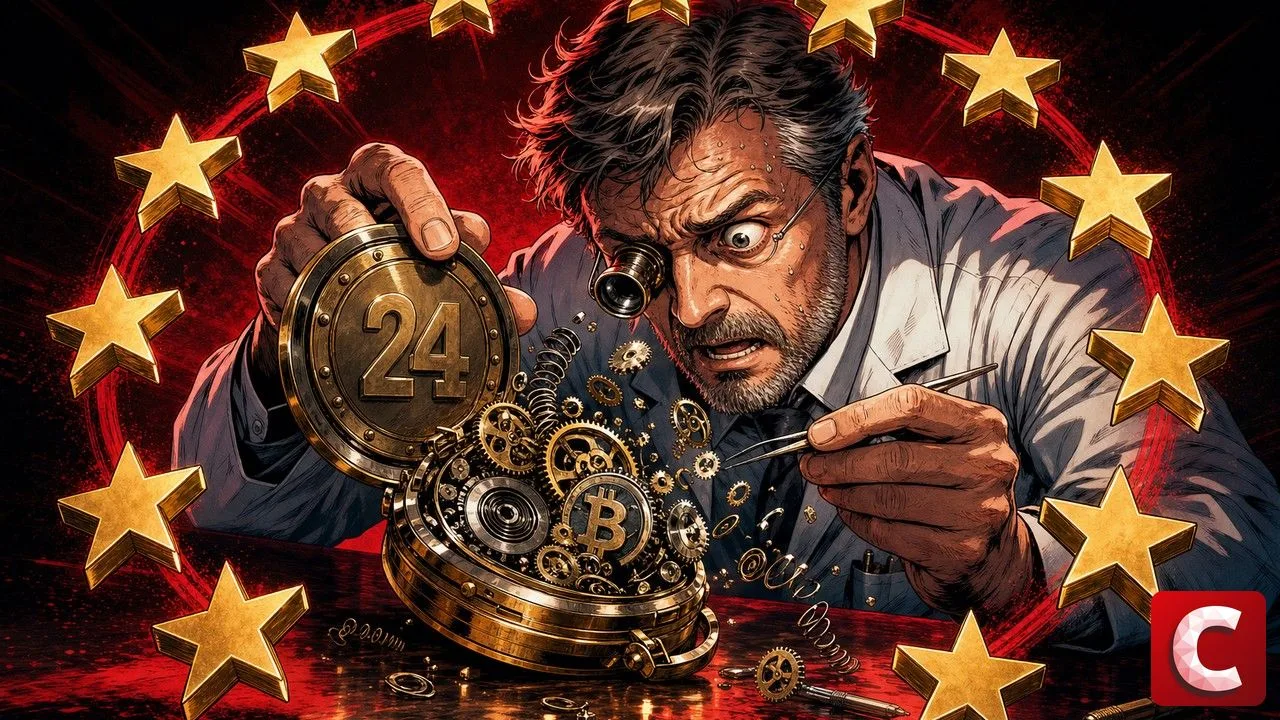
Since September 11, 2026, any company selling a crypto wallet inside the European Union has to report an actively exploited wallet flaw in under 24 hours. The duty comes from the Cyber Resilience Act and covers hardware devices and software clients alike. Missing the deadline exposes a manufacturer to a fine of up to 15 million euros or 2.5% of worldwide annual turnover.
Key Takeaways
- Early warning within 24 hours, full notification within 72 hours, final report within 14 days.
- An unreported wallet flaw can cost 15 million euros or 2.5% of global turnover.
- Non-EU manufacturers are caught the moment their product reaches the European market.
Get an AI Summary of This Article
ChatGPTBrussels Puts Device Makers on a Stopwatch
The European cyber resilience regulation took force on December 10, 2024, but its reporting duties only became binding on September 11, 2026. The text as published in the Official Journal of the European Union was never written for crypto. It covers every “product with digital elements” made available on the European market, a bracket wide enough to hold a cold storage device and a browser extension at the same time.
The clock on a wallet flaw starts the moment the manufacturer becomes aware of it. Within 24 hours, an early warning goes to ENISA and to the national incident response team through the single reporting platform the European agency now operates. A detailed notification follows within 72 hours. The final report lands 14 days after mitigation becomes available, and within one month for the most severe incidents.
The rest of the regime is still fifteen months out. Security-by-design requirements and certification duties only bite on December 11, 2027, on the application calendar the European Commission publishes. Lawmakers deliberately front-loaded incident transparency ahead of the technical obligations, reversing the order much of the industry had asked for. That preference for legible risk is a Brussels habit: the ECB built its multi-issuance stablecoin position on the same reasoning, without waiting for a specific failure.
This lands on an ecosystem already two years into a regulatory grind. The MiCA regime pushed a slice of European holders toward self-custody, with 70% of funds pulled from affected platforms moving into personal wallets. Those same wallets now sit inside a second regulation, which closes the loop: self-custody stops being a regulatory blind spot.
A Wallet Flaw Now Carries a 15 Million Euro Ceiling
The penalty schedule follows the template of every major European regulation. Sitting on a wallet flaw and breaching Articles 13 and 14, which govern manufacturer duties and vulnerability handling, exposes a firm to an administrative fine capped at 15 million euros or 2.5% of worldwide annual turnover, whichever is higher. Filing incorrect, incomplete or misleading information sits under a separate ceiling of 5 million euros.
Those numbers are not hypothetical. Austria’s regulator issued the first MiCA fine against Bitpanda without waiting out a grace period. The same pattern can repeat here, with one structural difference: the trigger is no longer a missing licence but a missed deadline, which is a timestamped fact a regulator can establish without qualifying anything.
Micro and small enterprises get a carve-out from the fines tied specifically to the 24-hour early warning. The duty to disclose a wallet flaw still applies to them in full. Mid-sized firms and large manufacturers get no accommodation at all.
Geographic reach is the part most operators underestimate. The regulation follows the product into whichever market it is offered on, wherever the head office sits. A company domiciled in Singapore, Switzerland or Delaware falls under the European regime as soon as its wallet is available in the Union. That extraterritorial logic already forced platforms to rework their European footprint, as Binance France showed when the MiCA licence failed to arrive by the July 1 cutoff.
Also on Cryptonomic:
- Privacy Coin Zcash Climbs Into the Top 10
- German Crypto Tax Ends the One-Year Exemption
- 263,000 Solana Tokens Were Minted in a Single Day
What Ledger and Trezor Owners Will Actually Notice
For the end user, the first change is one of tempo. Until now, a wallet flaw could be found, patched quietly, and disclosed once the fix had shipped. The new regime makes that sequence unlawful once the vulnerability is being actively exploited. The report goes to the regulator first, but the text also requires manufacturers to inform affected users and point them to available mitigations.
Recent history explains why this is sensitive. Breaches at suppliers working with Trezor and BitBox showed that a compromise does not have to touch private keys: it can run through a subcontractor, a customer database or an emailing channel, then feed targeted campaigns. The 24-hour rule attacks exactly that window, the stretch where an attacker holds information the victims do not.
Volume is the open question. Every wallet flaw disclosed under time pressure adds another public notice, and readers will have to separate a live incident from a theoretical weakness. A holder who gets four alerts a quarter stops opening them, which would turn the regulation against its own purpose.
Over the next few quarters the likelier effect is structural. Compliance costs money: a team able to triage a vulnerability in hours, a filing path into ENISA, documented follow-up. Small independent manufacturers may step back from the European market while established players turn the same burden into a selling point. The UK Parliament inquiry into banking access for crypto firms suggests consolidation-by-compliance is not a purely European story.
Follow the story on Cryptonomic.